
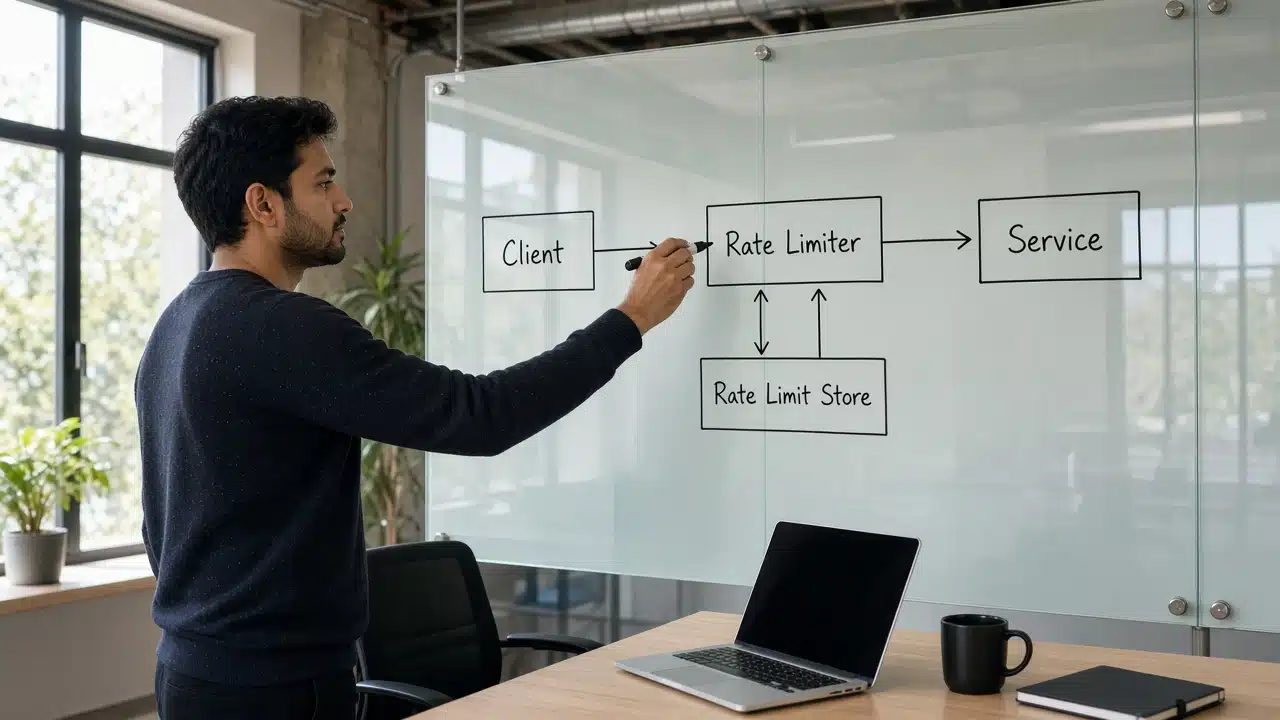
API Rate Limiting for SMB SaaS: Softix Budget–Burst–Shield
Published (planned): September 14, 2026 · Last updated: September 14, 2026 · Author: Softix
Category: SaaS Development
A single noisy tenant, a buggy client loop, or a credential-stuffing script can turn your “shared” multi-tenant API into an outage for everyone else. API rate limiting SaaS is not a gateway toggle you add after launch—it is a product contract: who gets how much capacity, how short spikes are absorbed, and what a clear 429 looks like when the budget is gone.
Softix’s Budget–Burst–Shield model is how we design fair per-key and per-tenant limits for SMB SaaS and custom software APIs. It is distinct from Softix Key–Store–Replay (API idempotency keys)—idempotency stops duplicate side effects on retries; rate limits stop unfair load before it melts the origin. It is also distinct from Softix outbound webhook Sign–Retry–DeadLetter—there you honor their 429/Retry-After as a publisher; here you emit honest limits as the API owner.
Primary references below cite IETF HTTP semantics for 429, AWS API Gateway throttling and usage plans, Cloudflare and NGINX rate-limit concepts, and public Stripe/Twilio rate-limit UX—not Softix throughput numbers. Softix does not invent RPS claims for Softix-hosted products. Scope MVP cost with Softix’s SaaS MVP scope & cost estimator when you are deciding how much limiter infrastructure belongs in v1 of your SaaS development roadmap.
Why SMB SaaS APIs need rate limits early
Fact (IETF). RFC 6585 §4 defines 429 Too Many Requests for clients that send too many requests in a given time. The response SHOULD explain the condition and MAY include a Retry-After header. RFC 9110 defines current Retry-After field semantics (delay-seconds or HTTP-date). Softix treats those as the baseline product UX for throttled callers—not an optional “nice to have.”
Softix analysis. A global IP throttle alone fails multi-tenant fairness: one authenticated integrator can starve neighbors; login abuse needs different keys than paid API keys; and support cannot explain a bare 503 with no retry hint. Budget–Burst–Shield separates capacity ownership, burst shaping, and honest abuse responses.
Softix Budget–Burst–Shield at a glance
| Softix step | What you do | Done when |
|---|---|---|
| Budget | Define per-API-key / per-tenant quotas (steady rate + daily/monthly caps) aligned to plan tiers | Documented limits in OpenAPI + billing/plan matrix; keys scoped to tenants |
| Burst | Allow short spikes with token-bucket (or carefully chosen window) algorithms so legitimate clients do not fail on page-load bursts | Burst capacity tested; origin protected from sustained overload |
| Shield | Layer edge/WAF + gateway + app limits; return clear 429 + Retry-After + machine-readable body |
Abuse paths blocked; integrators can back off without guessing |
Step 1 — Budget: per-key and per-tenant quotas
Fact (AWS API Gateway). Amazon documents that you can protect APIs with throttling and quotas, and that usage plans with API keys can set target request rates and quota limits for customers. Throttling uses a token bucket model (steady rate plus burst capacity). AWS also notes that usage-plan throttles are best-effort targets—not a substitute for cost controls or WAF protections. See Throttle requests to your REST APIs and Usage plans and API keys.
Softix Budget rules (analysis)
- Key limits by tenant + API key (or OAuth client), not only by IP. Anonymous and auth routes get separate policies.
- Publish a plan matrix: free / starter / growth with steady RPS (or RPM) and optional daily request quotas. Softix does not invent Softix customer RPS figures—use your capacity model and load tests.
- Separate expensive routes (search, export, report generation, bulk write) with tighter budgets than cheap GETs.
- Expose remaining budget when you can (for example
X-RateLimit-Limit,X-RateLimit-Remaining,X-RateLimit-Resetstyle headers)—match the style mature APIs document so SDKs can adapt. - Align billing: if a customer buys a higher tier, the Budget layer must change with the plan without a redeploy ceremony.
Softix judgment. A global RPS ceiling may protect your AWS account throttle (API Gateway documents account-level defaults such as 10,000 RPS with token-bucket burst in many Regions—confirm current quotas). It does not protect tenant A from tenant B. Softix Budget is the fairness layer.
Step 2 — Burst: token bucket and short spikes without melting origin
Fact (algorithms in production docs). AWS API Gateway describes token-bucket throttling: tokens refill at a steady rate; a burst parameter is bucket capacity. NGINX’s limit_req module documents a leaky-bucket approach with rate and optional burst (see ngx_http_limit_req_module). Cloudflare’s engineering writing contrasts leaky-bucket accuracy with approximate sliding-window counters for large-scale edge counting; Cloudflare WAF rate-limiting rules let you set characteristics, period, requests-per-period, and mitigation behavior (see Cloudflare rate limiting rules).
Softix Burst design checklist (analysis)
- Choose one primary algorithm per layer and document it. Softix often uses token bucket (or gateway equivalent) for authenticated API keys so clients can “save” short bursts after idle periods, and a stricter edge rule for unauthenticated paths.
- Burst ≠ infinite. Burst capacity should cover realistic client patterns (dashboard hydrate, mobile resume) without allowing sustained 10× steady rate.
- Protect expensive work separately. Cap concurrent heavy jobs; rate limits alone will not save you from N large exports started at once.
- Test the cliff. Load-test at 80%, 100%, and 120% of Budget; verify which requests get
429, which headers appear, and that legitimate neighbors stay healthy. - Do not copy a payments blog’s narrative structure. Softix Burst is your product capacity model—cite Stripe/Twilio only as examples of how clear public docs teach integrators to behave.
Product UX examples (public vendor docs, not Softix metrics). Stripe’s rate limits docs describe global/endpoint limits, 429, Stripe-Rate-Limited-Reason, and exponential backoff with jitter. Twilio REST best practices and error 20429 cover concurrency-aware 429 handling and headers such as Twilio-Concurrent-Requests. Softix recommends the same honesty: tell the client why and when to retry.
Step 3 — Shield: edge + app + clear 429 UX
Softix Shield layers (analysis)
- Edge / WAF — block obvious floods, credential stuffing, and scraper patterns (Cloudflare-style rate limiting rules by IP, path, or JA3/JA4 where available). Softix does not claim a specific Softix WAF rule pack as a compliance certificate.
- API gateway / reverse proxy — enforce Budget and Burst close to the edge (API Gateway usage plans, NGINX
limit_req, Envoy local rate limit, etc.). - Application — enforce tenant-aware quotas for business units the edge cannot see (seat, workspace, expensive method). Keep the decision keyed off authenticated identity.
- Response contract — return
429with explanatory body,Retry-Afterwhen you can compute it, and stable error codes your SDK maps to backoff. Per RFC 6585, do not rely on caches storing429responses.
Softix 429 UX packet
- HTTP status:
429 Too Many Requests(prefer this over opaque503for quota exhaustion when the client can safely retry later). - Headers:
Retry-After(seconds or HTTP-date); optional rate-limit remaining/reset headers your docs promise. - Body: machine-readable
error, humanmessage, optionaltype(rate_limit,quota_exceeded,concurrency_limit). - Docs: official backoff guidance—honor
Retry-After; else exponential backoff + jitter; never tight retry loops. - Support: admin view of which key/tenant hit which limit in the last hour.
Softix judgment. Shield without Budget creates unexplained bans. Budget without Shield fails when attackers never authenticate. Burst without Shield lets “friendly” clients still crush neighbors during a launch spike.
Design checklist Softix uses on SMB SaaS builds
| Check | Pass criteria |
|---|---|
| Identity key | Limits keyed by tenant + API key/OAuth client; IP only as secondary for anonymous routes |
| Plan matrix | Steady rate + optional quota published per tier; expensive routes called out |
| Algorithm | Token bucket / leaky bucket / sliding window choice documented per layer |
| Burst proof | Synthetic burst tests pass without origin CPU cliff for neighbor tenants |
| 429 contract | Retry-After + JSON error; OpenAPI examples; SDK backoff helper |
| Edge overlap | WAF/gateway rules do not contradict app limits without a documented precedence |
| Observability | Metrics: 429 rate by tenant/key/route; alert on sudden spikes |
| Honesty | No fabricated Softix throughput SLAs; publish only measured limits |
30-day Budget–Burst–Shield plan
| Week | Focus | Done when |
|---|---|---|
| 1 | Budget inventory | Routes ranked by cost; draft plan matrix; identity keys chosen |
| 2 | Burst implementation | Gateway or app token-bucket live in staging with burst tests |
| 3 | Shield + UX | Edge rules + 429/Retry-After contract in OpenAPI; SDK backoff |
| 4 | Prove fairness | Noisy-neighbor test; support runbook; plan-upgrade path verified |
How this pairs with Softix API reliability posts
- Idempotency (Key–Store–Replay) — clients retry safely after timeouts; rate limits tell them when to slow down. Softix still expects idempotency keys on mutating POSTs when retries happen after a
429. - Outbound webhooks (Sign–Retry–DeadLetter) — as a publisher, Softix honors customer
429andRetry-After; as an API owner, Softix emits them. Do not conflate the two runbooks. - Multi-tenant architecture — pool vs silo decisions change blast radius; rate limits are the shared-pool fairness control Softix insists on early.
Limits and honesty checks
- Best-effort gateway quotas (as AWS documents for usage plans) are not billing meters or absolute DDoS shields—pair with WAF and cost alerts.
- Softix will not invent “X RPS Softix cluster” marketing numbers or fake customer conversion claims.
- Rate limits do not replace authentication, authorization, fraud checks, or idempotency.
- Lock/concurrency errors (Stripe documents some
429lock cases separately from rate limits) need their own client guidance when you mirror that pattern.
FAQ
Should every SMB SaaS start with API Gateway usage plans?
Not always. Softix starts with Budget identity (tenant + key) and a documented algorithm. If you already sit behind API Gateway, usage plans are a strong fit; if you are on Cloudflare + app servers, edge rules plus an app limiter can be enough for early stages—as long as Shield UX stays clear.
Is a fixed window (reset every minute) good enough?
It is simple and often wrong at the edges (clients can double-tap at window boundaries). Softix prefers token bucket or sliding/approximate sliding windows for public APIs unless you explicitly accept fixed-window bias and document it.
What status code should Softix return when the daily quota is exhausted?
Prefer 429 with a body that distinguishes rate vs quota, plus Retry-After pointing to reset when known. Some teams use 403 for hard plan denials—if you do, document it; Softix default for temporary throttle/quota is 429 per RFC 6585 intent.
How is this different from Softix API idempotency keys?
Idempotency prevents duplicate side effects. Rate limiting prevents unfair or abusive load. You almost always need both on a serious mutating API.
Do Softix rate limits replace a WAF?
No. Shield is layered: WAF/edge for abuse patterns, gateway/app for tenant Budgets. One layer alone is incomplete.
Next step
Softix designs Budget–Burst–Shield into SMB SaaS APIs from Building 41, Johar Town, Lahore—so fair limits ship before noisy neighbors define on-call. Estimate scope with the MVP estimator, explore Softix SaaS development and custom software development, then Let’s Talk. Building 41, Johar Town, Lahore · +92 332 6444418.
Share


